When computing becomes infrastructure: sovereign AI and business continuity
· By Antonio Sedino · Reinventy Solutions Corp.
Data centers are strategic infrastructure exposed to conflict, attacks and failures. A tested internal AI capability can help companies protect industrial knowledge and keep essential activities available.
A company can own its data and still be unable to work without the operational availability of distant infrastructure. That dependency deserves attention now, as artificial intelligence becomes part of engineering, software development, maintenance and knowledge management.
The large models offered by OpenAI, Anthropic and Google through Gemini provide remarkable capabilities. The industrial problem arises when a useful service becomes indispensable to production and the company has no practical alternative when it is unavailable. The decisive question is concrete: what work could we continue tomorrow if the connection to our AI provider stopped?
Data centers have a geography, and geography matters
Digital computation depends on buildings, power, cooling, connectivity and people. A physical crisis can therefore spread far beyond the place where it occurs. Documented events show that data centers have also entered the geography of conflict.
On 8 October 2026, Reuters reported that Yandex had suspended operations at its Sasovo center after a drone attack and a fire. The following day, the agency reported a second attack on the Kaluga site, which the company said had been partially disabled. This does not mean that all Yandex services disappeared or prove that its AI systems were destroyed.
ANSA’s 19 October report on Kyiv adds a Russian claim concerning an unidentified data center. It should be treated as a statement by a party to the conflict, rather than independent technical confirmation.
Amazon has also stated that the conflict disrupted its AWS Bahrain Region, while helping customers migrate to other regions. This directly confirms that geopolitical risk can become an operational problem for users of digital services.
These incidents do not establish that every data center is a military target or that one interruption stops an entire industry. They show that continuity of computation belongs in the assessment of industrial risk.
The risk exists without a conflict
The strategic value of infrastructure is also evident in cybercrime. The joint FBI, CISA and Australian authorities’ advisory on Play ransomware, updated in June 2025, describes attacks targeting ESXi virtualization environments. The target can be the ability to run many applications, alongside the data used for extortion.
Other incidents have different causes. The OVHcloud fire in Strasbourg in March 2021 destroyed most of SBG2 and damaged SBG1: a physical incident, rather than evidence of an attack. AWS’s account of the Northern Virginia disruption in October 2025 instead documents a defect in DynamoDB DNS automation and consequences for dependent services: an operational failure, rather than military action.
War, extortion, fire and technical error require different defenses. For company management, however, they share a question: which essential functions remain available when a central dependency fails?
AI dependency can become production dependency
An assistant can accelerate research or help write code. Once integrated into design stages, document workflows and everyday tools, its unavailability can slow or interrupt particular activities. The impact depends on how those processes were built; there is no universal deadline after which every company will stop without AI.
It is therefore necessary to distinguish the highest quality available in normal conditions from the minimum capability needed to continue. A powerful external model may be a reasonable choice for some tasks. For others, it is essential to retain tools, documents and executable models under the company’s control, with known and tested limits.
A local alternative may be less impressive in general conversation and still valuable for searching internal manuals, retrieving approved procedures, assisting a technician or comparing a design revision. It must be evaluated on those tasks, with appropriate human checks, without automatically assigning it the performance of the model it replaces.
An internal micro data center as working capability
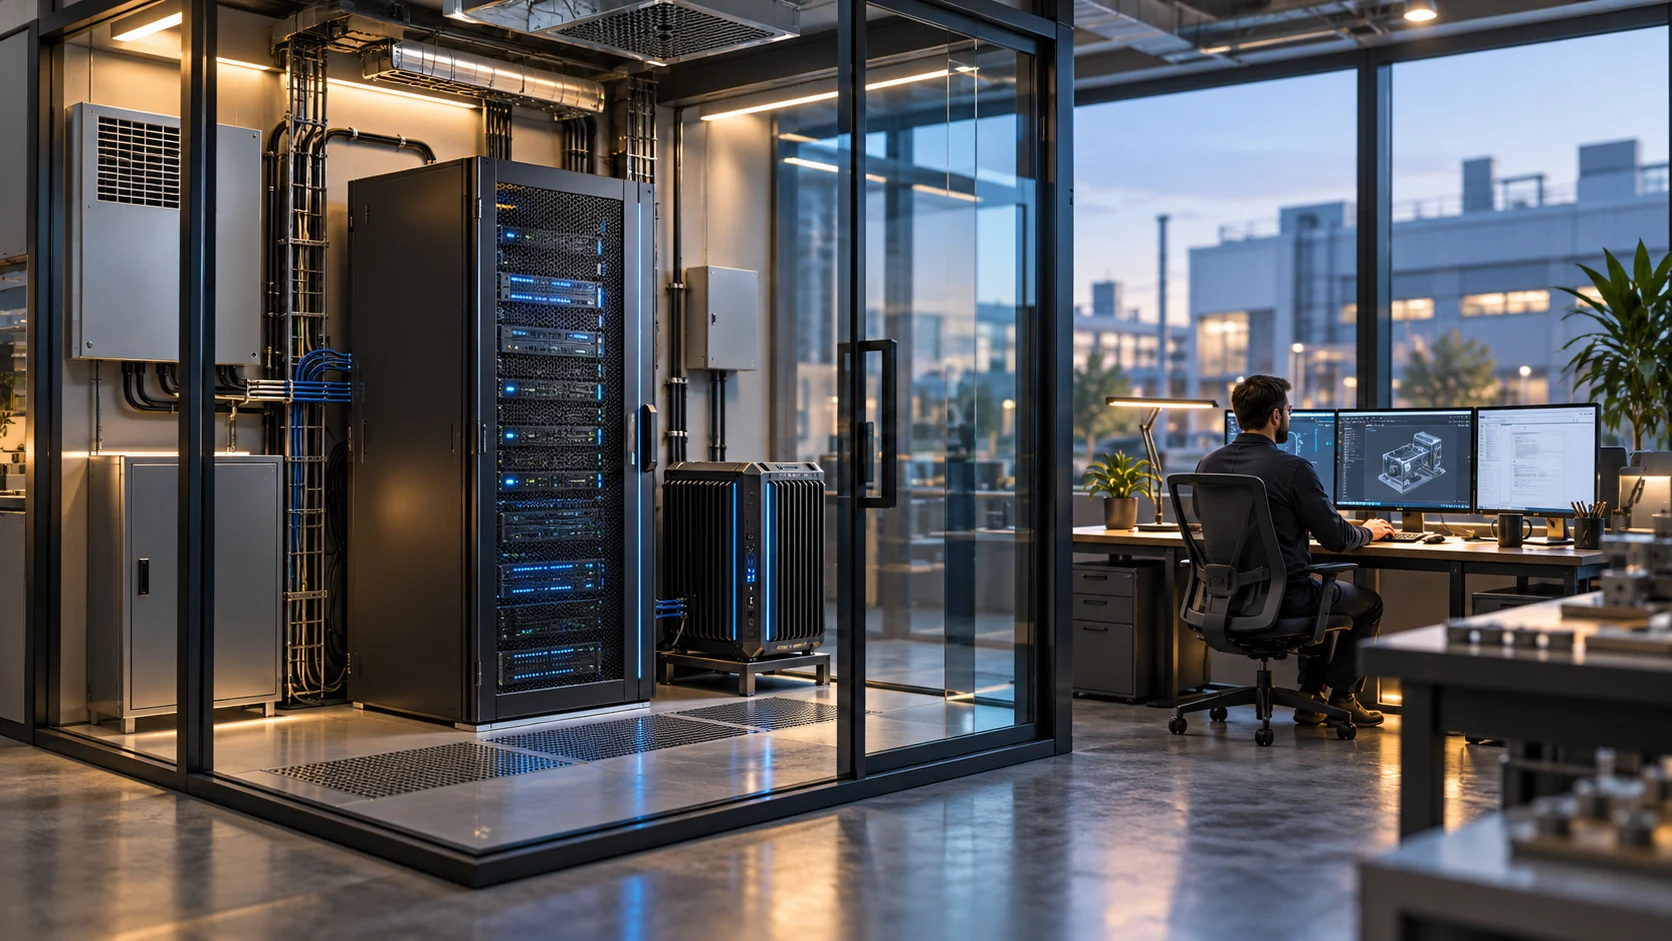
This is the direction of Reinventy’s work on sovereign intelligence: designing internal capability proportionate to company processes, from an edge node near a machine to a micro data center for models, archives and business applications.
Compact size does not remove the engineering requirements. The chosen models need sufficient resources, suitable power and cooling, access management, verified updates and people able to maintain the system. A peak performance figure does not establish how many cases an office can complete or how many checks a laboratory can carry out.
For materials, software and algorithms, this architecture can also reduce the need to transfer confidential formulations and knowledge externally. Confidentiality must be built through rules and controls; purchasing a server is insufficient. Likewise, a model with available weights still requires verification of its license and terms of use.
Sovereignty also means being able to recover elsewhere
Concentrating everything in one building would exchange one dependency for another point of vulnerability. The Ukrainian experience is instructive in the opposite direction too: Microsoft documented in 2022 that distributing government infrastructure across the European cloud helped maintain operations after attacks on local systems.
The principle is to retain control and recovery options across different failures. Useful internal capability can coexist with external services, protected copies at a separate location and recovery procedures that do not all depend on the same account, connection or provider.
The most convincing evidence is an agreed exercise: isolate external services in a controlled environment, restart necessary applications and perform essential tasks using representative data. Quality, completion times, sustainable load and information recovery need to be measured. Models, document indexes, identities, licenses and tools must remain available within the boundary intended to operate autonomously.
This is consistent with the continuity planning discipline described by NIST: start from critical functions, establish recovery priorities and test procedures. The existence of a backup alone does not establish that the company can resume work.
Retaining the practical ability to continue
For Reinventy, the commercial proposition must start with the processes to protect: identify essential activities, design suitable sovereign infrastructure and agree on operational and recovery tests. The maturity and performance of each solution must be demonstrated in the customer’s context.
The objective is to let companies use advanced innovation while retaining their own working capability, including when they must accept more limited performance. Protecting industrial secrets and protecting productive continuity become two aspects of the same investment: retaining control of the company’s operational future.
Sources and verification
Research updated on 19 October 2026. Conflict incidents are distinguished from criminal attacks and operational failures; claims remain attributed. The architectural proposal and industrial assessment are the author’s analysis.
Reuters, 8 October 2026 — Sasovo: https://www.marketscreener.com/news/drones-hit-yandex-site-in-first-major-attack-on-russian-data-hub-ce785dded089f423
Reuters, 9 October 2026 — Kaluga: https://www.marketscreener.com/news/russia-s-yandex-says-second-data-centre-was-hit-by-drone-attack-ce785ddfde81f426
ANSA, 19 October 2026 — Kiev: https://www.ansa.it/sito/notizie/mondo/2026/10/19/missili-russi-su-kiev-un-morto-e-otto-feriti_880ccfc3-f526-4c4a-9def-79024e582454.html
Amazon — AWS Bahrain Region disrupted by ongoing conflict: https://www.aboutamazon.com/news/aws-bahrain-region-middle-east-conflict
FBI, CISA and ASD’s ACSC — Play Ransomware: https://www.cisa.gov/news-events/cybersecurity-advisories/aa23-352a
OVHcloud — Strasbourg fire information: https://corporate.ovhcloud.com/en-gb/newsroom/news/informations-site-strasbourg/
AWS — DynamoDB disruption report for Northern Virginia: https://aws.amazon.com/message/101925/
Microsoft, 22 June 2022 — Defending Ukraine: https://blogs.microsoft.com/on-the-issues/2022/06/22/defending-ukraine-early-lessons-from-the-cyber-war/
NIST SP 800-34 Rev. 1 — Contingency Planning Guide: https://csrc.nist.gov/pubs/sp/800/34/r1/upd1/final